Self-Custody Slack Alternative
September 28, 2026 | Category: Diode
Self-Custody Slack Alternative
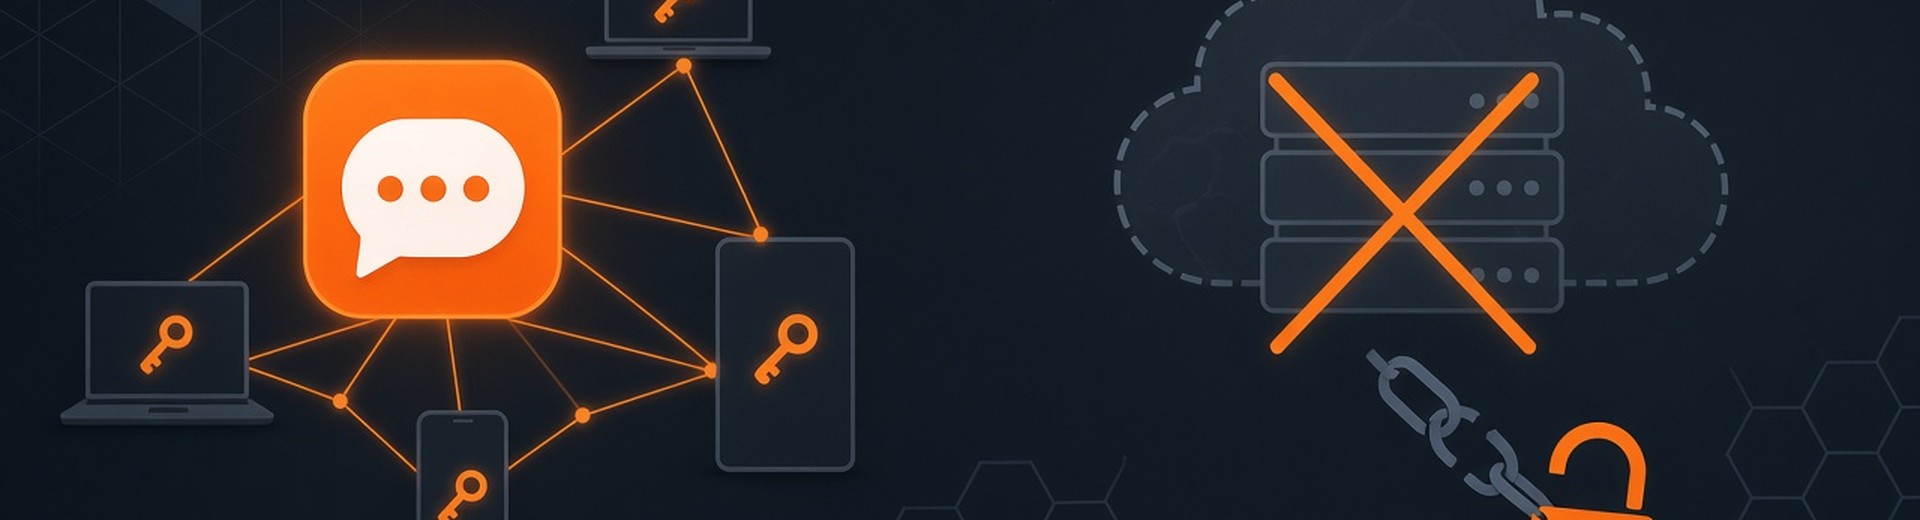
A self-custody Slack alternative keeps encryption keys on participating devices instead of giving a collaboration vendor a universal workspace key. With Diode Collab, chat and files are local-first and encrypted, and no chat, files, accounts, or PII are held on a Diode vendor server for the vendor to read in the normal service model. This is different from self-hosting a chat server: self-hosting means your organization runs the server, and that server still has to store, secure, back up, and deliver collaboration data.
That distinction matters when a team searches for a private Slack alternative, encrypted Slack alternative, or secure Slack alternative. The question is not only whether a product uses encryption. It is where the keys live, who operates the infrastructure, and who can technically access the workspace. For background, read our encrypted Slack alternative guide, Is Slack End-to-End Encrypted?, and Can Slack Read My Messages?.
Self-Custody, Local-First, and Self-Hosted Mean Different Things
These terms are often treated as interchangeable, but they describe different trust and operating models.
Self-custody or device-held keys means the team controls the keys needed to open its collaboration content. In Diode Collab, keys remain on participating devices. Chat and files can synchronize in encrypted form between authorized devices, while the Diode vendor does not hold a readable server-side workspace containing the team’s chat, files, accounts, or PII.
Local-first describes where the product starts and where data remains useful: on participating devices rather than in a central cloud database that must be contacted for every operation. It does not mean that networks or synchronization cease to exist; it means working data and keys are not designed around a vendor-readable central archive.
Self-hosted means that your organization operates the server or servers. A self-hosted Matrix deployment, Rocket.Chat installation, or Mattermost instance can give an administrator control over the operating system, database, network, retention rules, and upgrades. It is still a server-based service. The server may hold accounts, encrypted or plaintext message records, files, logs, and metadata, depending on the product and configuration.
There is also a fourth category: SaaS with E2EE. A hosted provider runs the infrastructure, while encryption is intended to keep message and file content unreadable to that provider. That can be a strong choice, but teams should check the key design, account recovery, device enrollment, backups, metadata, file handling, integrations, and whether the provider can access any usable copies. E2EE does not automatically mean that the vendor holds no infrastructure or no information about the service.
How the Models Compare
| Model | Who runs the infrastructure? | Key and data boundary | Main trade-off |
|---|---|---|---|
| Diode Collab self-custody | Local-first network with participating team devices | Keys stay on devices; no chat, files, accounts, or PII on a Diode vendor server | Teams take more responsibility for devices, membership, and recovery |
| Slack | Slack operates the SaaS service | Slack’s infrastructure is part of the workspace access boundary for normal delivery, search, sync, and integrations | Excellent SaaS convenience and administration, but vendor-readable workspace content |
| Typical self-hosted Matrix, Rocket.Chat, or Mattermost | Your organization or a hosting provider | The server remains part of the data and metadata boundary; E2EE varies and is not the default assumption for every deployment | Maximum server control requires patching, backups, monitoring, hardening, and incident response |
| Hosted SaaS with E2EE | A commercial provider | Message content may be protected from provider decryption, but the provider still runs infrastructure and may handle accounts, routing, metadata, or encrypted blobs | Less operational work than self-hosting, with a provider trust boundary to evaluate |
The choice depends on the boundary your team is trying to change: self-custody removes a vendor-readable workspace, self-hosting controls the server, and Slack prioritizes a mature app ecosystem and centralized administration.
What Diode Collab Provides
Encrypted chat inside Zones
Diode Collab organizes collaboration through Zones: shared security perimeters for a team, project, or group. Members participate in a Zone, and encrypted conversations stay associated with the devices and people authorized for that perimeter. A Zone is not a Slack workspace, a Matrix room, or a public community. It is Diode Collab’s device-oriented membership model.
Teams can separate projects into different Zones and make membership a deliberate security decision without making a phone number or email address the foundation of every identity. The product is aimed at teams that want conversation context without a central vendor database of readable messages.
Encrypted files beside conversations
Slack is valuable partly because messages, links, and files share one familiar workspace. A privacy-focused replacement has to address files too. Diode Collab is designed for encrypted file sharing alongside team chat, with content kept on participating devices rather than uploaded into a Diode vendor archive for search or administration.
Self-custody narrows vendor access, but teams still need to decide who has an authorized device, how devices are protected, what happens when a laptop is lost or a member leaves, and which recovery process fits the project.
ZTNA and remote access
Collaboration often includes more than text and attachments. Diode Collab combines encrypted collaboration with ZTNA-style remote access, allowing a field team to reach selected internal dashboards or project tools through controlled tunnels rather than exposing them broadly to the public internet. Teams still secure the destination, connected device, and Zone membership, but can consider chat, files, and internal-tool access together.
No phone number or email required
Diode Collab does not require a phone number or email address for team identity. That helps teams avoid making a personal contact detail the root of access to sensitive work and can support pseudonymous or compartmentalized projects. Device-based identity makes recovery and replacement a team responsibility, however; conventional SaaS may feel easier if provider-managed password resets are the priority.
When Slack Wins
A self-custody architecture is not automatically a better replacement for every Slack deployment. Slack wins when the organization values a mature, centralized SaaS experience more than removing the vendor from the content access path. Its marketplace and integrations connect ticketing, CRM, calendars, code hosting, incident response, analytics, bots, and custom workflows, while familiar channels, threads, search, notifications, guest access, and account recovery reduce rollout friction.
Enterprise administration can also be the requirement. Centralized retention, organization-wide search, eDiscovery, legal holds, audit tooling, DLP, and administrator visibility are useful when the organization is required to inspect or preserve content. Those capabilities depend on Slack being able to process workspace data and are not compatible with a strict “the vendor cannot read the workspace” requirement.
Choose Slack when its integrations, marketplace, polished UX, or enterprise controls are the actual priority and the organization accepts Slack’s trust boundary. Choose a self-custody Slack alternative when vendor-readable chat and centralized PII are the risks you are trying to remove.
When Self-Hosted Matrix, Rocket.Chat, or Mattermost Wins
Self-hosting is the better direction when your organization wants direct control of the server environment and has the staff to operate it. A self-hosted Matrix deployment can provide an open protocol, federation, and control over homeserver placement. Rocket.Chat and Mattermost can be attractive when a team wants Slack-like channels, plugins, and customization inside infrastructure it manages.
The benefit is control over the operating system, network, database, storage, backups, retention, access policies, upgrade schedule, and internal integrations. The cost is operational responsibility: someone must patch and harden the host, monitor capacity, protect credentials, test restores, manage media and databases, handle incidents, and keep the service available. E2EE may be available in a particular deployment, but self-hosting by itself does not prove that only participants can read messages.
Self-hosting is therefore a server-control choice, not a synonym for self-custody. A team that does not want to run chat infrastructure may prefer Diode Collab’s local-first model. A team that specifically wants to operate its own infrastructure may prefer Matrix, Rocket.Chat, or Mattermost. For a deeper comparison with Matrix, see Diode Collab vs Element.
When Hosted E2EE Is the Right Compromise
Some teams want end-to-end encrypted messaging but do not want to manage servers. A hosted E2EE product can provide polished applications, support, and managed availability while cryptography is intended to keep message content out of the vendor’s readable path. That is a legitimate compromise, but ask whether keys remain only on devices, whether recovery creates a provider-held copy, how devices are trusted, where files and thumbnails are processed, what metadata the provider sees, and how integrations access content. A hosted E2EE service can protect content while still operating a conventional cloud control plane.
For examples of this hosted-versus-device-held distinction, read Diode Collab vs Wire. For the broader Slack decision, see Diode Collab vs Slack.
Security Benefits and Responsibilities
The central benefit of self-custody is a narrower trust boundary. A Diode vendor server is not intended to hold a readable database of your team’s chat, files, accounts, or PII, and device-held keys mean the platform operator is not in the normal position to decrypt the workspace. That reduces exposure when a vendor is breached or asked for content it never held in readable form.
Self-custody does not prevent endpoint compromise, device failure, a member copying plaintext, or malware capturing content after decryption. Teams adopting local-first collaboration should define device protections, Zone membership changes, offboarding steps, and recovery procedures before putting sensitive material into a Zone.
The architecture also changes familiar SaaS conveniences: centralized global search, automatic history on every device, vendor-managed account resets, eDiscovery, and broad third-party integrations may be more limited or work differently. Self-custody is valuable when key control and reduced vendor custody outrank those conveniences. Do not infer ISO, SOC 2, or HIPAA certificates unless Diode publishes evidence for the specific claim; evaluate your own policies, devices, data, and legal obligations alongside the architecture.
Diode Collab Pricing
Diode Collab offers three paid plans:
| Plan | Monthly per user | Yearly per user / month |
|---|---|---|
| Group | $3 | $2.50 |
| Team | $10 | $8.50 |
| Business | $15 | $12.50 |
The yearly column is the per-user monthly equivalent when billed yearly. Review the Diode Collab pricing page for current plan details and limits. Compare the full operating model, including device management and recovery, rather than comparing only a seat price against a hosted chat plan or a self-hosted server license.
Who Should Choose a Self-Custody Slack Alternative?
Diode Collab is a strong fit when:
- The team wants encryption keys held on participating devices.
- Chat and files should not be stored on a Diode vendor server for the vendor to read.
- Accounts and PII should not sit in a Diode vendor database.
- Zones provide a useful way to separate people, projects, and security perimeters.
- Encrypted files and ZTNA remote access belong beside team chat.
- A phone number or email address should not be required for team identity.
- The organization can take responsibility for endpoint security, membership, device availability, and recovery.
Slack may be the better choice when deep integrations, marketplace applications, centralized search, eDiscovery, or familiar enterprise administration are non-negotiable. A self-hosted Matrix, Rocket.Chat, or Mattermost deployment may be better when full control of server infrastructure is the priority and the organization has the operations capacity. Hosted E2EE may be the right middle ground when managed availability matters more than eliminating the provider’s infrastructure trust boundary.
Frequently Asked Questions
Is self-custody the same as self-hosting?
No. Self-custody focuses on control of keys and collaboration data; self-hosting focuses on who operates the server. A self-hosted chat service can give your organization server control while still storing data on that server.
Can Diode Collab replace every Slack integration?
No. Slack has a larger marketplace, mature integrations, polished workflows, and centralized administration. Diode Collab is a better fit when device-held keys, encrypted files, Zones, and ZTNA matter more than reproducing every SaaS integration.
Does a self-custody product remove all security risk?
No. It reduces vendor custody and keeps keys on participating devices, but compromised endpoints, lost devices, unsafe members, and poor recovery processes remain risks. Self-custody changes who must manage those risks.
Try Diode Collab
If your team wants a private Slack alternative with device-held keys, encrypted chat and files, Zones, and ZTNA remote access, review Diode Collab pricing and download Diode Collab for your team’s devices. Start with a small Zone, define recovery and offboarding procedures, and compare the result with the centralized Slack or self-hosted server model your team uses today.